62443 Design Specialist Study Guide
A condensed guide to the ISA/IEC 62443 Cybersecurity Design Specialist exam, written to go with the practice exam in this repository. Last reviewed October 2026.
Not affiliated with or endorsed by ISA or IEC. This guide summarizes the standards in its own words; it doesn't replace them.
On this page
- Exam at a glance and a 7-day game plan
- The ISA lifecycle and where design fits
- From risk assessment to CRS (62443-3-2)
- Security levels and system requirements (62443-3-3)
- Components and suppliers (4-1, 4-2, 2-4, ISASecure)
- Conceptual vs detailed design
- Network segmentation and firewalls
- Secure remote access
- System hardening
- Intrusion detection and monitoring
- Testing: CFAT, CSAT and SL-A validation
- Exam traps and tie-breakers
- Sources
Exam at a glance and a 7-day game plan
You must pass 100 closed-book multiple-choice questions in 2 hours, about 72 seconds each. ISA reports only pass or fail.
| Item | What to expect |
|---|---|
| Questions | 100 multiple choice, closed book |
| Time | 2 hours (72 s per question on average) |
| Delivery | Meazure Learning test center, or online with live remote proctoring (LRP) |
| Result | Pass or fail; a failed attempt shows % correct per domain, not a score |
| Prerequisite | Fundamentals Specialist certificate already earned |
| Retakes | Allowed inside the 6-month eligibility window; USD 120 (members) or 150 (non-members) each |
| Content basis | IC34 IACS Cybersecurity Design & Implementation learning objectives |
Sources: ISA certificate FAQ · ISA exams and testing · IC34 course page. Fees and policies change; check ISA's site.
Pacing. Take a first pass at about 50 s per question and flag anything that runs past 90 s. That leaves about 30 minutes for flagged items and a final check. Answer every question; a blank can only cost you.
What gets tested. The IC34 objectives: interpret risk assessment results, write a CRS, build a conceptual design from it, explain the security development lifecycle, configure and commission a basic firewall, design secure remote access, write a hardening specification, deploy a basic network IDS, and plan and run a CFAT or CSAT.
Practice exam. The practice exam in this repository has 203 original questions across ten domains: timed 100-question mocks, drills by domain, and a retake list of every miss. Progress saves in the browser you use.
7-day plan
| Day | Study | Practice in the exam app |
|---|---|---|
| 1 | Skim this guide end to end | 40-question baseline across all domains; note your 3 weakest |
| 2 | 62443-3-2 workflow, CRS, zones and conduits | Risk results & CRS |
| 3 | Security levels; 62443-3-3 FRs, SRs, REs | Security levels & requirements |
| 4 | 62443-4-1, 4-2, 2-4; conceptual vs detailed design | Supplier SDL; Conceptual & detailed design |
| 5 | Firewalls, remote access, hardening, IDS | Those four domains, then full timed mock #1 |
| 6 | CFAT, CSAT, SL-A validation | Testing domain, then review every missed question |
| 7 | Traps section and the key tables only | Full mock #2 early in the day, then stop |
If the exam is sooner, merge days 2 to 4 and keep at least one full timed mock. For LRP, run Meazure's system check and reread the invitation instructions a day early.
The ISA lifecycle and where design fits
Design is the Develop & Implement phase: it turns the CRS from the Assess phase into countermeasures. It then proves them in CFAT and CSAT before handing over to Maintain.
| Phase | Key steps | Main outputs |
|---|---|---|
| Assess | Identify the SUC; initial (high-level) risk assessment; zones and conduits; detailed risk assessment; document requirements | Zone and conduit model, SL-T per zone and conduit, CRS |
| Develop & Implement | Conceptual design; detailed design; procure or build; install and commission; verify and validate (CFAT, CSAT) | Design specifications, hardening specs, firewall rule sets, test plans and reports, SL-A |
| Maintain | Operate, monitor, patch, back up, manage change, respond to incidents, reassess, decommission | Logs, MOC records, audit results, updated risk assessment |
Who does what
| Role | Responsibility in design | Main parts |
|---|---|---|
| Asset owner | Accountable for IACS risk throughout. Sets tolerable risk; approves the CRS, residual risk and handover | 2-1, 3-2 |
| Integration service provider | Designs, implements and verifies the automation solution against the CRS | 2-4, 3-3 |
| Maintenance service provider | Keeps countermeasures effective in operation | 2-4 |
| Product supplier | Builds products with security capabilities (SL-C) under a secure development lifecycle; ships updates and guidelines | 4-1, 4-2 |
One organization can hold several roles, but accountability for the IACS stays with the asset owner.
Parts you must place instantly
| Part | Title | Use in design |
|---|---|---|
| 1-1 | Terminology, concepts and models | Zones, conduits, SLs, FRs, reference model |
| 2-1 | Security program requirements for IACS asset owners | Owner policies the design must follow |
| 2-3 | Patch management in the IACS environment | Patch strategy |
| 2-4 | Security program requirements for IACS service providers | Integrator capabilities, SP.01 to SP.12 |
| 3-1 | Security technologies for IACS | Technology categories to choose from |
| 3-2 | Security risk assessment for system design | ZCR 1 to 7, SL-T, CRS |
| 3-3 | System security requirements and security levels | SRs and REs per SL; SL-C and SL-A |
| 4-1 | Secure product development lifecycle requirements | Supplier SDL, 8 practices |
| 4-2 | Technical security requirements for IACS components | CRs for the four component types |
Principles that decide close answers
- Defense in depth: layered physical, procedural, network, host, application and data controls.
- Least privilege and least functionality.
- Essential functions come first. Security must not block safety functions, operator view or control unless a risk assessment supports it.
- In IACS the priority is availability and integrity before confidentiality.
From risk assessment to CRS (62443-3-2)
62443-3-2 has seven zone and conduit requirements (ZCRs). The designer's input is ZCR 6, the CRS, which the asset owner approves in ZCR 7.
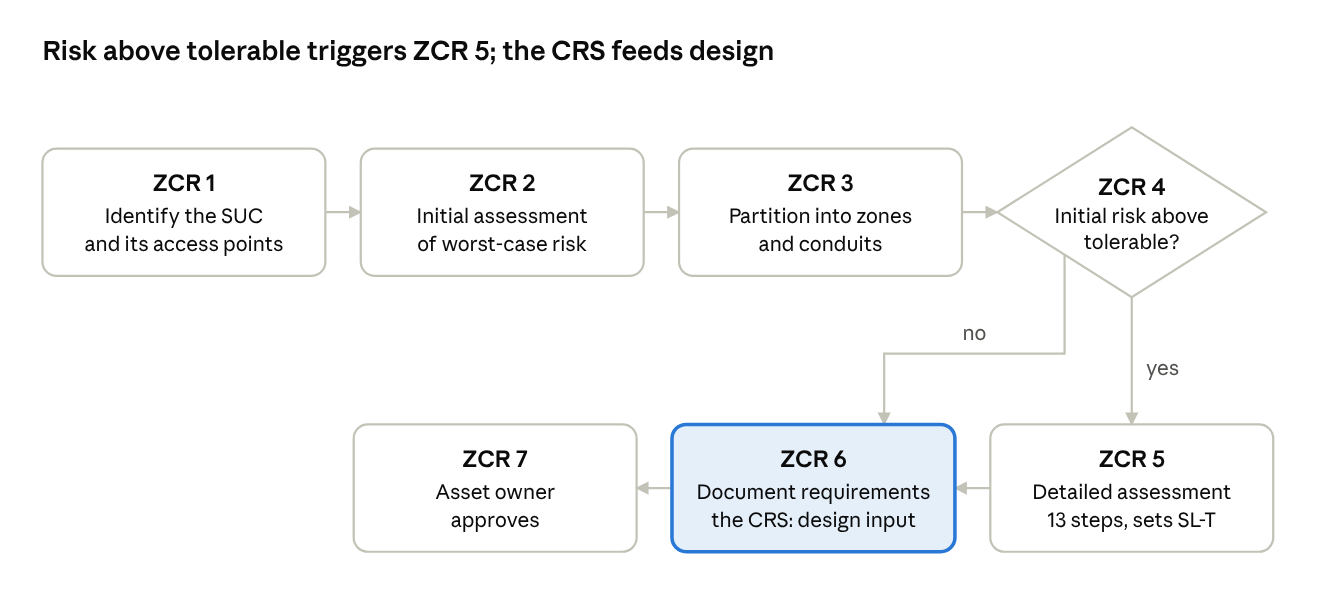
ZCR 4 decides whether the detailed assessment runs. Either way, the documented CRS is what the asset owner approves and the designer builds from.
| ZCR | Requirement | Output |
|---|---|---|
| 1 | Identify the SUC (1.1: perimeter and access points) | SUC boundary and access points |
| 2 | Initial cybersecurity risk assessment | Worst-case unmitigated risk |
| 3 | Partition the SUC into zones and conduits (3.1 to 3.6) | Zone and conduit model |
| 4 | Compare initial risk to tolerable risk | Whether a detailed assessment is needed |
| 5 | Detailed cybersecurity risk assessment (5.1 to 5.13) | Residual risk, SL-T, extra countermeasures |
| 6 | Document cybersecurity requirements, assumptions and constraints (6.1 to 6.9) | The CRS |
| 7 | Asset owner approval | Approved results |
ZCR 3: what must be separated (3.2 to 3.6). Business from IACS assets; safety-related assets; temporarily connected devices; wireless devices; devices connected via external networks. Memory hook: B-S-T-W-E.
ZCR 5: the 13 detailed steps, in order
- Identify threats
- Identify vulnerabilities
- Determine consequence and impact
- Determine unmitigated likelihood
- Determine unmitigated cybersecurity risk
- Determine SL-T
- Compare unmitigated risk with tolerable risk
- Identify and evaluate existing countermeasures
- Reevaluate likelihood and impact
- Determine residual risk
- Compare residual risk with tolerable risk
- Identify additional countermeasures
- Document and communicate results
SL-T is set at step 6, before existing countermeasures are credited.
ZCR 6: what the CRS contains (6.1 to 6.9). The CRS itself; SUC description; zone and conduit drawings; zone and conduit characteristics; operating environment assumptions; threat environment; organizational security policies; tolerable risk; regulatory requirements.
Zone and conduit characteristics (6.4) include the name or ID, accountable organization, logical and physical boundaries, safety designation, access points, data flows, connected zones and conduits, asset list and criticality, SL-T, applicable requirements and policies, assumptions and external dependencies.
Reading a CRS as a designer
- The SL-T vector per zone and conduit sizes the countermeasures.
- Every CRS requirement needs a traceable design element and, later, a test.
- Assumptions (physical security, trained staff, vendor support) are design constraints. If one fails, the residual risk changes.
- A zone groups assets that share security requirements. A conduit groups the communication channels between zones that share requirements.
- Tolerable risk is the asset owner's call, never the integrator's.
Security levels and system requirements (62443-3-3)
Each zone and conduit gets an SL-T vector across the seven FRs. The design passes when SL-A meets SL-T in every FR, using component capability (SL-C) plus compensating countermeasures.
| SL | Protects against | Attacker profile |
|---|---|---|
| 0 | No specific requirement | None |
| 1 | Casual or coincidental violation | Accidents, errors |
| 2 | Intentional violation, simple means | Low resources, generic skills, low motivation |
| 3 | Intentional violation, sophisticated means | Moderate resources, IACS-specific skills, moderate motivation |
| 4 | Intentional violation, sophisticated means | Extended resources, IACS-specific skills, high motivation |
Three SL types
- SL-T (target): what a zone or conduit needs, from the 3-2 risk assessment.
- SL-C (capability): what a system (3-3) or component (4-2) can deliver when properly configured.
- SL-A (achieved): what the deployed zone or conduit actually delivers, verified at CSAT and kept in operation.
- Rule: select SL-C ≥ SL-T per FR or add compensating countermeasures, then verify SL-A ≥ SL-T.
The SL vector is written in FR order {IAC UC SI DC RDF TRE RA}, for example SL-T = {3 3 2 1 3 2 3}. Compare FR by FR; never average or take the maximum.
| FR | Name | SRs | Typical countermeasures |
|---|---|---|---|
| 1 IAC | Identification and authentication control | 1.1 to 1.13 | Domain accounts, MFA for remote users, PKI, password policy |
| 2 UC | Use control | 2.1 to 2.12 | RBAC, session lock, audit events, timestamps |
| 3 SI | System integrity | 3.1 to 3.9 | Antimalware, allowlisting, integrity checks, input validation |
| 4 DC | Data confidentiality | 4.1 to 4.3 | Encryption in transit and at rest, purging on disposal |
| 5 RDF | Restricted data flow | 5.1 to 5.4 | Segmentation, firewalls, DMZ, unidirectional gateways |
| 6 TRE | Timely response to events | 6.1 to 6.2 | Log access, continuous monitoring, IDS and SIEM |
| 7 RA | Resource availability | 7.1 to 7.8 | DoS protection, backup and recovery, least functionality, inventory |
There are 51 SRs in total.
High-yield SRs and REs: the SL where each first appears
| Requirement | First required at |
|---|---|
| SR 1.1 RE1 Unique identification and authentication of human users | SL2 |
| SR 1.1 RE2 MFA for untrusted networks | SL3 |
| SR 1.1 RE3 MFA for all networks | SL4 |
| SR 1.2 Software process and device identification and authentication | SL2 |
| SR 1.13 RE1 Explicit access request approval (untrusted networks) | SL2 |
| SR 2.1 RE1 Authorization for all users; RE2 permission mapping to roles | SL2 |
| SR 2.1 RE3 Supervisor override | SL3 |
| SR 2.1 RE4 Dual approval | SL4 |
| SR 2.6 Remote session termination | SL2 |
| SR 2.7 Concurrent session control | SL3 |
| SR 2.8 RE1 Centrally managed, system-wide audit trail | SL3 |
| SR 2.12 Non-repudiation | SL3 |
| SR 3.1 RE1 Cryptographic integrity protection | SL3 |
| SR 3.2 RE1 Malicious code protection on entry and exit points | SL2 |
| SR 3.2 RE2 Central management and reporting of malicious code protection | SL3 |
| SR 4.1 RE1 Confidentiality at rest or in transit via untrusted networks | SL2 |
| SR 4.1 RE2 Confidentiality across zone boundaries | SL4 |
| SR 5.1 RE1 Physical network segmentation | SL2 |
| SR 5.1 RE2 Independence from non-control system networks | SL3 |
| SR 5.1 RE3 Logical and physical isolation of critical networks | SL4 |
| SR 5.2 RE1 Deny by default, allow by exception | SL2 |
| SR 5.2 RE2 Island mode; RE3 Fail close | SL3 |
| SR 5.3 RE1 Prohibit all person-to-person communications | SL3 |
| SR 6.2 Continuous monitoring | SL2 |
| SR 7.1 RE1 Manage communication loads | SL2 |
| SR 7.3 RE1 Backup verification | SL2 |
| SR 7.3 RE2 Backup automation | SL3 |
| SR 7.8 Control system component inventory | SL2 |
Pattern: SL2 brings unique identities, deny-by-default and monitoring. SL3 brings MFA from untrusted networks, central audit and antimalware, cryptographic integrity, island mode and fail close. SL4 brings MFA everywhere, dual approval and confidentiality across zone boundaries.
Compensating countermeasure: used instead of, or in addition to, a missing inherent capability. Example: a legacy PLC with no authentication sits behind a conduit firewall with protocol inspection, plus physical access control. Document it, test it, and get the asset owner to accept the residual risk.
Essential functions: security must not stop a safety function, operator view or control. That is why fail close (SR 5.2 RE3) must not interfere with the SIS, and why operator HMIs often alarm instead of locking accounts.
Components and suppliers (4-1, 4-2, 2-4, ISASecure)
Suppliers prove their process with 62443-4-1 and their products with 62443-4-2. Integrators prove their capabilities with 62443-2-4.
62443-4-1: eight practices
| # | Practice | IDs | Remember |
|---|---|---|---|
| 1 | Security management | SM-1 to SM-13 | Process, roles, expertise, dev environment, private keys, third-party components |
| 2 | Specification of security requirements | SR-1 to SR-5 | Product security context, threat model, requirements review |
| 3 | Secure by design | SD-1 to SD-4 | Secure design principles, defense in depth design, design review |
| 4 | Secure implementation | SI-1 to SI-2 | Implementation review, secure coding standards |
| 5 | Security verification and validation testing | SVV-1 to SVV-5 | Requirements, threat mitigation, vulnerability and penetration testing; independent testers |
| 6 | Management of security-related issues | DM-1 to DM-6 | Receive, review, assess, address, disclose |
| 7 | Security update management | SUM-1 to SUM-5 | Qualify, document and deliver updates; timely patches |
| 8 | Security guidelines | SG-1 to SG-7 | Defense in depth, expected environment, hardening, disposal, operation, accounts |
The integrator consumes SG-2 (defense in depth measures expected in the environment) and SG-3 (hardening guidelines) in the design. SUM-1 (update qualification) is why you install only vendor-qualified patches.
Maturity levels (4-1 and 2-4)
| ML | Name | Meaning |
|---|---|---|
| 1 | Initial | Ad hoc, often undocumented; unpredictable results |
| 2 | Managed | Written, controlled process; trained staff; may not yet be practiced |
| 3 | Defined (Practiced) | Practiced and repeatable across the organization, with evidence |
| 4 | Improving | Effectiveness measured and continuously improved |
62443-4-2: four component types
| Type | Prefix | Examples |
|---|---|---|
| Software application | SAR | HMI or SCADA software, historian application, antivirus |
| Embedded device | EDR | PLC, DCS controller, safety controller, IED |
| Host device | HDR | Engineering workstation, operator station, server |
| Network device | NDR | Switch, router, firewall, wireless access point |
- Common requirements are CR x.y, numbered like the 3-3 SRs. Type-specific ones carry the prefix, such as NDR 5.2 zone boundary protection.
- 4-2 adds device-level items absent from 3-3: physical diagnostic and test interfaces (2.13), support for updates (3.10), tamper resistance (3.11), roots of trust (3.12, 3.13) and boot integrity (3.14).
- Common component security constraints: CCSC 1 support of essential functions, CCSC 2 compensating countermeasures, CCSC 3 least privilege, CCSC 4 development under a 4-1 process.
62443-2-4: 12 service provider areas. SP.01 Solution staffing · SP.02 Assurance · SP.03 Architecture · SP.04 Wireless · SP.05 SIS · SP.06 Configuration management · SP.07 Remote access · SP.08 Event management · SP.09 Account management · SP.10 Malware protection · SP.11 Patch management · SP.12 Backup/restore.
ISASecure certifications
| Certification | Certifies | Basis |
|---|---|---|
| SDLA | A supplier's development process | 4-1 |
| CSA | An off-the-shelf component, at a capability level | 4-2 |
| SSA | A control system, at a capability level | 3-3 |
In procurement, ask for the SL-C per FR, any ISASecure certificate, the supplier's security guidelines, its patch qualification process and its support lifecycle.
Conceptual vs detailed design
Conceptual design says which kind of countermeasure goes where for every CRS requirement. Detailed design says which product, configured how, in enough detail to build and test.
| Conceptual design | Detailed design | |
|---|---|---|
| Input | Approved CRS: SL-T, zones and conduits, assumptions, policies | Approved conceptual design |
| Answers | What type of control, in which zone or conduit | Which product, which settings |
| Typical content | Zone and conduit architecture, control per zone and conduit, remote access and monitoring approach, gaps and compensating measures | Drawings and IP plan, firewall rule sets, hardening spec per component, account and role matrix, backup design, IDS placement, bill of materials, procedures |
| Vendor specific | No | Yes |
| Used for | Budget, early review, owner approval | Procurement, build, CFAT and CSAT test cases |
| Document | Conceptual design specification | Detailed design specification |
Technology categories (62443-3-1)
- Authentication and authorization
- Filtering, blocking and access control (firewalls, VLANs, proxies)
- Encryption and data validation
- Management, audit, measurement, monitoring and detection
- IACS computer software (operating system, antimalware, allowlisting)
- Physical security controls
Selecting a technology
- It delivers the SL-C needed in the FRs it addresses.
- The control system vendor supports it, and it has no unacceptable impact on performance, latency or availability.
- It fails in a way that preserves essential functions.
- Site staff can maintain it for the life of the system: updates, signatures, licenses, skills.
- Proven in OT beats newest in IT.
Traceability and approval
- Keep a matrix: CRS requirement, design element, test case, result.
- The design records assumptions, residual risks and compensating countermeasures, and the asset owner approves it.
- Changes after approval go through management of change.
Network segmentation and firewalls
Traffic between enterprise and control networks terminates in a DMZ. Every zone boundary denies by default, and every allowed flow has a documented reason.
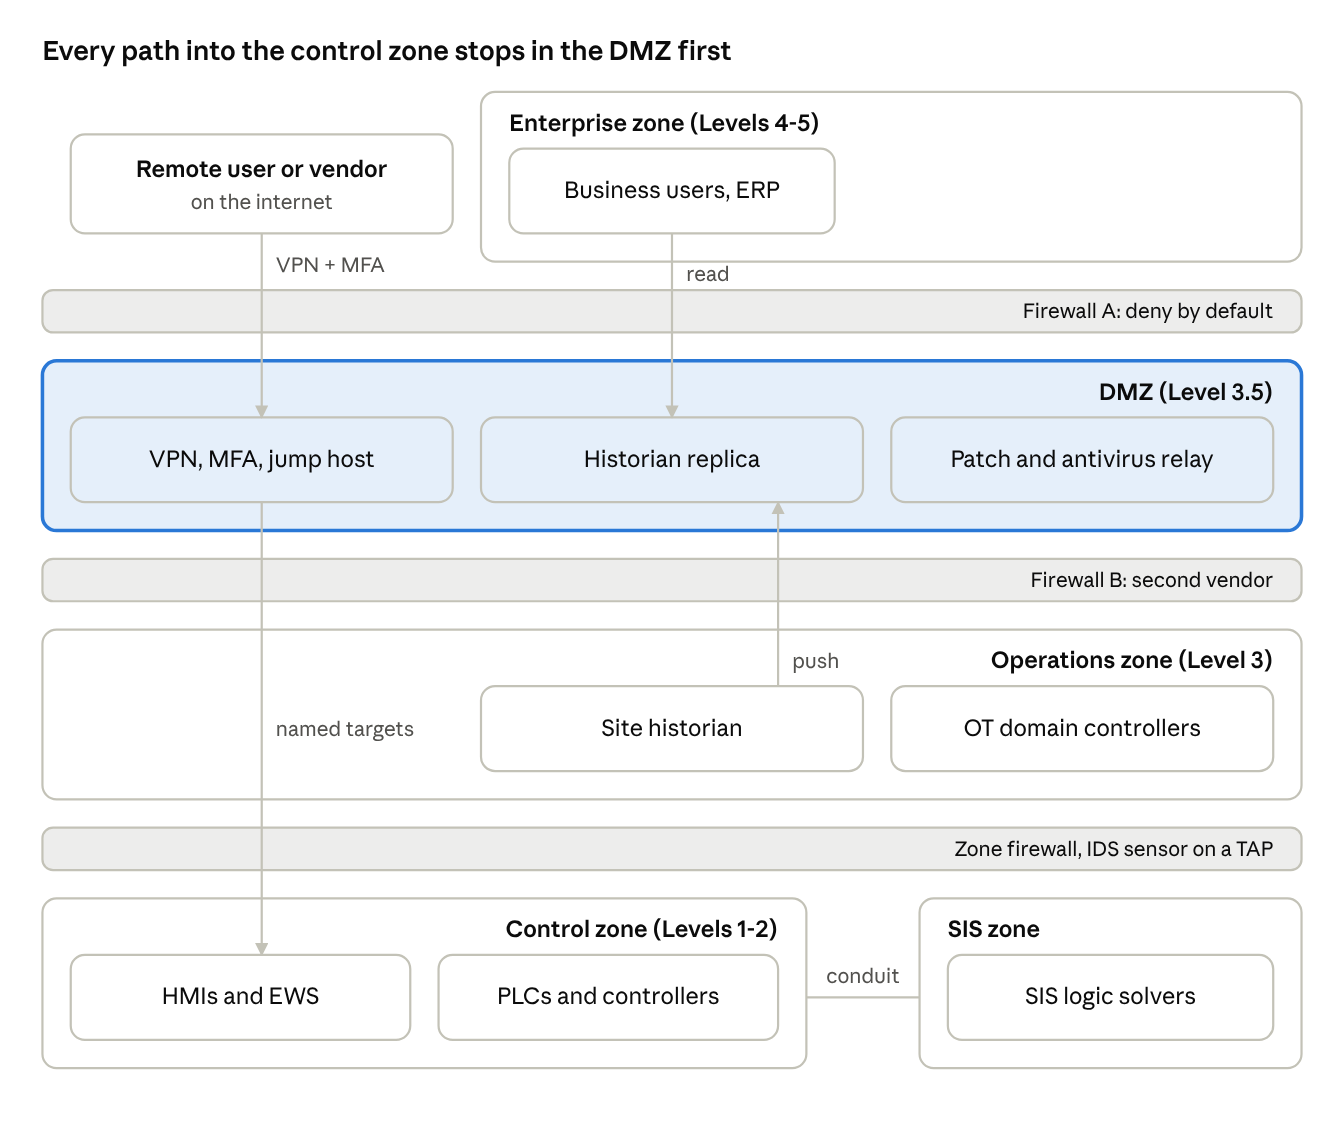
Enterprise users read the DMZ replica, the historian pushes to it, and remote users reach only named targets through the jump host. The SIS keeps its own zone and conduit.
| Level | Contents | Typical zone |
|---|---|---|
| 4 to 5 | Enterprise IT, business systems, internet | Enterprise |
| 3.5 | Historian replica, patch and antivirus relays, jump host | DMZ |
| 3 | Site operations: historian, OT domain controllers, MES | Operations |
| 2 | Supervisory: HMI, SCADA, engineering workstations | Control |
| 1 | Basic control: PLCs, DCS controllers; SIS logic solvers | Control; separate SIS zone |
| 0 | Process: sensors and actuators | Field |
DMZ rules
- Nothing passes straight through. Enterprise talks to the DMZ, and the DMZ talks to the control network.
- Prefer connections initiated from the more trusted side, such as the historian pushing to its DMZ replica.
- Two firewalls from different vendors add depth; a single three-legged firewall is the cheaper, weaker option.
- No dual-homed hosts bridging zones; they bypass the firewall.
Rule-base design
- Deny by default, allow by exception (SR 5.2 RE1), outbound as well as inbound.
- Each rule names a specific source, destination and service. No "any". Each has a documented justification and owner.
- Specific rules before general ones: the first match wins and an implicit deny ends the list.
- Log denied traffic and important permits.
- Use protocol-aware inspection where it helps, such as allowing only Modbus read function codes from the historian.
- Manage firewalls from a management network only, with individual accounts and MFA.
- Review the rule base periodically and remove unused, shadowed and expired temporary rules.
Commissioning a firewall
- Load vendor-qualified firmware, change default credentials, disable unused services and interfaces.
- Restrict management access; set NTP; send logs to the central log server or SIEM.
- Load the approved rule set; back up the configuration under change control.
- Test that each permitted flow works and that sample denied flows are blocked and logged.
- Verify failover or fail-close behavior as designed; record the results.
Other boundary and network controls
- Unidirectional gateway (data diode): hardware-enforced one-way flow, the strongest way to push data out of a high-SL zone.
- VLANs are logical segmentation only. Inter-VLAN traffic still needs an access-control point.
- Switches: shut unused ports, port security or 802.1X, no auto-trunking, SSH and SNMPv3 only.
- Wireless gets its own zone (ZCR 3.5) behind a boundary device, with WPA2 or WPA3-Enterprise and 802.1X.
- The SIS gets its own zone (ZCR 3.3) with a minimal conduit to the BPCS. Restrict SIS engineering access, and never let fail close disturb safety functions.
Secure remote access
Remote users never land in the control zone directly. They authenticate with MFA into a remote-access zone, then reach only approved targets through a jump host, inside an approved time window, with the session logged.
Reference path
- The user requests access for a task and time window, and the asset owner approves it (SR 1.13 RE1).
- An encrypted VPN or secure gateway terminates in a remote-access zone at the DMZ, never inside the control zone. External connections are their own zone (ZCR 3.6).
- MFA at the gateway (SR 1.1 RE2 for untrusted networks).
- The user works from a hardened jump host, which breaks the protocol path. No tunnel reaches Level 2 or 1.
- The inner firewall allows only jump host to named target on named ports.
- Sessions are monitored or recorded, time out (SR 2.5) and can be terminated (SR 2.6).
- Access is disabled when the window closes; logs go to the SIEM and are reviewed.
Design rules
- Individual named accounts with least privilege; no shared vendor logins.
- Vendor access is off by default and enabled on demand, not always on.
- No modems or cellular routers that bypass the DMZ.
- Disable split tunneling; check endpoint posture where possible.
- File transfers go through a staging point with malware scanning (SR 3.2 RE1).
- Keep the SIS out of routine remote access.
- 62443-2-4 SP.07 sets the matching service provider requirements.
System hardening
A hardening specification states, per component type, the approved baseline: what is removed, disabled, changed and enabled. It derives from the supplier's hardening guidelines (4-1 SG-3) and is verified at CFAT.
What a hardening spec contains
- Scope: component type, model, OS or firmware version.
- References: supplier security guidelines, site policy, benchmarks the vendor supports.
- Settings: allowed services, ports and protocols (SR 7.7 least functionality); accounts; password and lockout policy; logging; time sync; malware protection; removable media; host firewall; BIOS or UEFI; banner (SR 1.12).
- A verification method for every setting, so the CFAT can test it.
- Exceptions, each with its compensating countermeasure.
By component type
| Component | Key hardening steps |
|---|---|
| Windows host | Remove unneeded roles and software; disable unused services and ports; operators as standard users with separate admin accounts; vendor-qualified antimalware or allowlisting; disable AutoRun; restrict USB storage; audit logging, NTP, log forwarding; lock BIOS or UEFI and enable secure boot |
| Network device | Change defaults; replace Telnet, HTTP and SNMPv1/v2c with SSH, HTTPS and SNMPv3; shut unused ports and park them in an unused VLAN; port security; central AAA with individual accounts; banner, syslog, NTP; back up the config |
| Controller (PLC, DCS) | Use the mode switch or protection levels to block remote program changes; disable unused services (web, FTP, SNMP); set passwords; load only vendor firmware with integrity checks |
Removable media policy and procedure
- Policy: who may use removable media, for what, and which approved devices.
- Technical: block USB mass storage on hosts by default.
- Procedure: scan media on a dedicated scanning station before use, and log every transfer. Prefer controlled file transfer through the DMZ.
- Requirement links: SR 2.3 portable and mobile devices; SR 3.2 RE1 entry and exit points; ZCR 3.4 temporarily connected devices.
Antimalware vs allowlisting
| Antivirus | Application allowlisting | |
|---|---|---|
| Works by | Signatures of known malware | Only approved executables run |
| Needs | Frequent, vendor-qualified signature updates | Updating the allowlist through MOC when software changes |
| Best fit | Hosts where updates are manageable | Static OT hosts such as HMIs and engineering stations |
Patching (62443-2-3)
- Install only vendor-qualified patches, after testing on a test or staging system.
- Deploy through MOC in a maintenance window, with a backup first.
- If a patch can't be installed, apply and document a compensating countermeasure.
- Patch and antivirus servers sit at Level 3 or in the DMZ and pull updates through the DMZ.
Intrusion detection and monitoring
In control zones, use a passive network IDS fed by TAPs or SPAN ports at conduits and core switches. Alerts go to a SIEM with synchronized time. Avoid inline blocking where a false positive could stop the process.
Placement
- At zone boundaries and conduits, such as DMZ to control and control to SIS.
- On core switches inside critical zones, to see east-west traffic, not only the perimeter.
- The sensor's monitoring interface has no IP address. Its management interface sits in a management zone.
| SPAN (mirror port) | Network TAP | |
|---|---|---|
| How | The switch copies traffic to a port | Passive hardware copies the link |
| Pros | No extra hardware; flexible | Sees every packet, adds no switch load, cannot inject traffic |
| Cons | Can drop packets under load; uses switch resources; easy to misconfigure | Extra hardware; installing it in line needs an outage |
| Signature-based | Anomaly-based | |
|---|---|---|
| Detects | Known attack and malware patterns | Deviations from a learned baseline: new hosts, connections, function codes |
| Strength | Few false positives on known threats | Finds novel attacks; suits predictable OT traffic |
| Weakness | Misses new attacks; needs rule updates | Learning period; alerts after legitimate changes |
IDS vs IPS. An IDS listens and alerts. An IPS sits in line and blocks, which adds latency and a failure point, and a false positive can drop control traffic. Keep blocking to less critical boundaries, if used at all.
Logging and time
- SR 2.8 auditable events; SR 2.8 RE1 central audit trail at SL3.
- SR 2.11 timestamps from a trusted time source inside OT, such as a GPS clock.
- SR 3.9 protects audit information; SR 6.1 gives read access to logs; SR 6.2 requires continuous monitoring at SL2.
- A host IDS adds file integrity monitoring and local log analysis.
Snort rule anatomy (header, then options):
alert tcp !10.10.3.20 any -> 10.10.2.0/24 502 (msg:"Modbus/TCP from non-historian host"; sid:1000001; rev:1;)Action, protocol, source IP and port, direction, destination IP and port, then options. Local rules use SIDs of 1,000,000 and above. Tune after a baseline period, and give every alert an owner and a triage procedure.
Testing: CFAT, CSAT and SL-A validation
CFAT proves the system as built meets the CRS before it ships. CSAT proves the installed, connected system still meets it on site. Together they establish SL-A against SL-T.
| CFAT | CSAT | |
|---|---|---|
| Where and when | Integrator facility or staging, before shipment | On site, after installation and integration, before handover |
| Proves | The system as built and configured meets the CRS and design | The installed system, with site connections and services, still meets them |
| Typical tests | Hardening baselines, accounts and roles, firewall rules on the staged network, malware protection, patch level, backup and restore, logging and time, vulnerability scan | Boundary firewalls to site networks, remote access path, site directory accounts, IDS and SIEM feeds, physical security, anything untestable at the factory, re-checks of items changed during installation |
| Active scanning | Acceptable on the staged system | Only before start-up or with owner approval; prefer passive methods on live systems |
What a test plan contains
- Scope, objectives and references (CRS, design specifications).
- Roles and witnesses: asset owner, integrator, supplier.
- Environment, tools and entry criteria.
- Test cases traced to CRS requirements: steps, expected result, actual result, pass or fail, evidence.
- Deviation and punch-list handling, retest, exit criteria and sign-off.
- Schedule and safety precautions, especially on site.
Validating SL-A with 62443-3-3
- For each zone and conduit, go FR by FR through the SRs and REs that its SL-T requires.
- Test or inspect each one.
- The SL-A for an FR is the highest level whose SRs and REs are all met, natively or through compensating countermeasures.
- Where SL-A falls short of SL-T: fix it, add a compensating countermeasure, or have the asset owner formally accept the residual risk.
| Requirement | Test | Pass criterion |
|---|---|---|
| SR 1.11 Unsuccessful login attempts | Enter a wrong password one more time than the limit | Account locks (or alarms on a critical HMI) and the event is logged |
| SR 5.2 RE1 Deny by default | Send an unapproved protocol from an enterprise host to a control host | Blocked and logged |
| SR 3.2 Malicious code protection | Check engine and signature versions; drop the EICAR test file on a test host | Detected and reported |
| SR 7.3 and 7.4 Backup and recovery | Restore a server from backup onto spare hardware | Returns to a known secure state |
Exam traps and tie-breakers
When two answers look right, pick the one that is risk-based, documented, approved by the asset owner, and keeps essential functions running.
Tie-breakers
- Risk assessment and CRS come before products. "Just buy a firewall" is rarely right.
- The asset owner sets tolerable risk and approves the CRS, the design, residual risk and handover. Integrators recommend.
- Availability and safety outrank confidentiality.
- Deny by default, least privilege, least functionality.
- On live systems, passive beats active: IDS over IPS, passive discovery over scanning.
- Vendor-qualified and tested before deployed: patches, antimalware, configuration changes.
- Compare SL vectors FR by FR. One FR short means the target is not met.
- Compensating countermeasures are valid when documented, verified and accepted.
Traps
- SL is technical capability (3-3, 4-2); ML is process maturity (4-1, 2-4).
- 3-2 is risk assessment for design, 3-3 system requirements, 4-2 component requirements, 4-1 the supplier's process, 2-4 the service provider, 2-1 the owner's program.
- SL-T is set per zone and per conduit, not per device or per plant.
- SL-C is what a product can do; SL-A is what the deployed configuration achieves.
- Traffic crosses the DMZ in two hops, never as one session.
- A VLAN is not physical segmentation.
- CFAT happens at the factory before shipment; CSAT happens on site.
- Remote access terminates in the DMZ, never in the control zone.
- An IPS at Level 1 or 2 is usually the wrong answer.
- Fail close (SR 5.2 RE3) must not interfere with the SIS.
- Critical operator HMIs alarm on failed logins rather than locking out.
- The initial risk assessment uses worst-case, unmitigated consequences.
Sources
- ISA certificate programs FAQ
- ISA certificate exams and testing
- IC34 course description
- ISA/IEC 62443 Cybersecurity Certificate Program
- ISA-62443-3-2 table of contents
- ISA-62443-4-1 table of contents
- ISAGCA Security Lifecycles white paper
- ISASecure certification programs
- 62443-3-3 SR and RE list (SCF mapping)
- 62443-3-3 Annex B SL mapping, teaching paraphrase
Other details are summarized from the 62443 standards. Check anything doubtful against your licensed copies.